Scans from the outside
Websites, APIs, every TCP port, encryption, and email and DNS, scanned on a schedule from our scanners, the way anyone on the internet reaches them.
Naxirion
Vulnerability Scanning
Vulnerability scanning you can believe.
Scans your websites, APIs, servers and email domains from the internet on a schedule, finds names under your domains you'd forgotten, and grades what it finds in plain English, including what it couldn't reach.
Open-source engines, run unmodified:
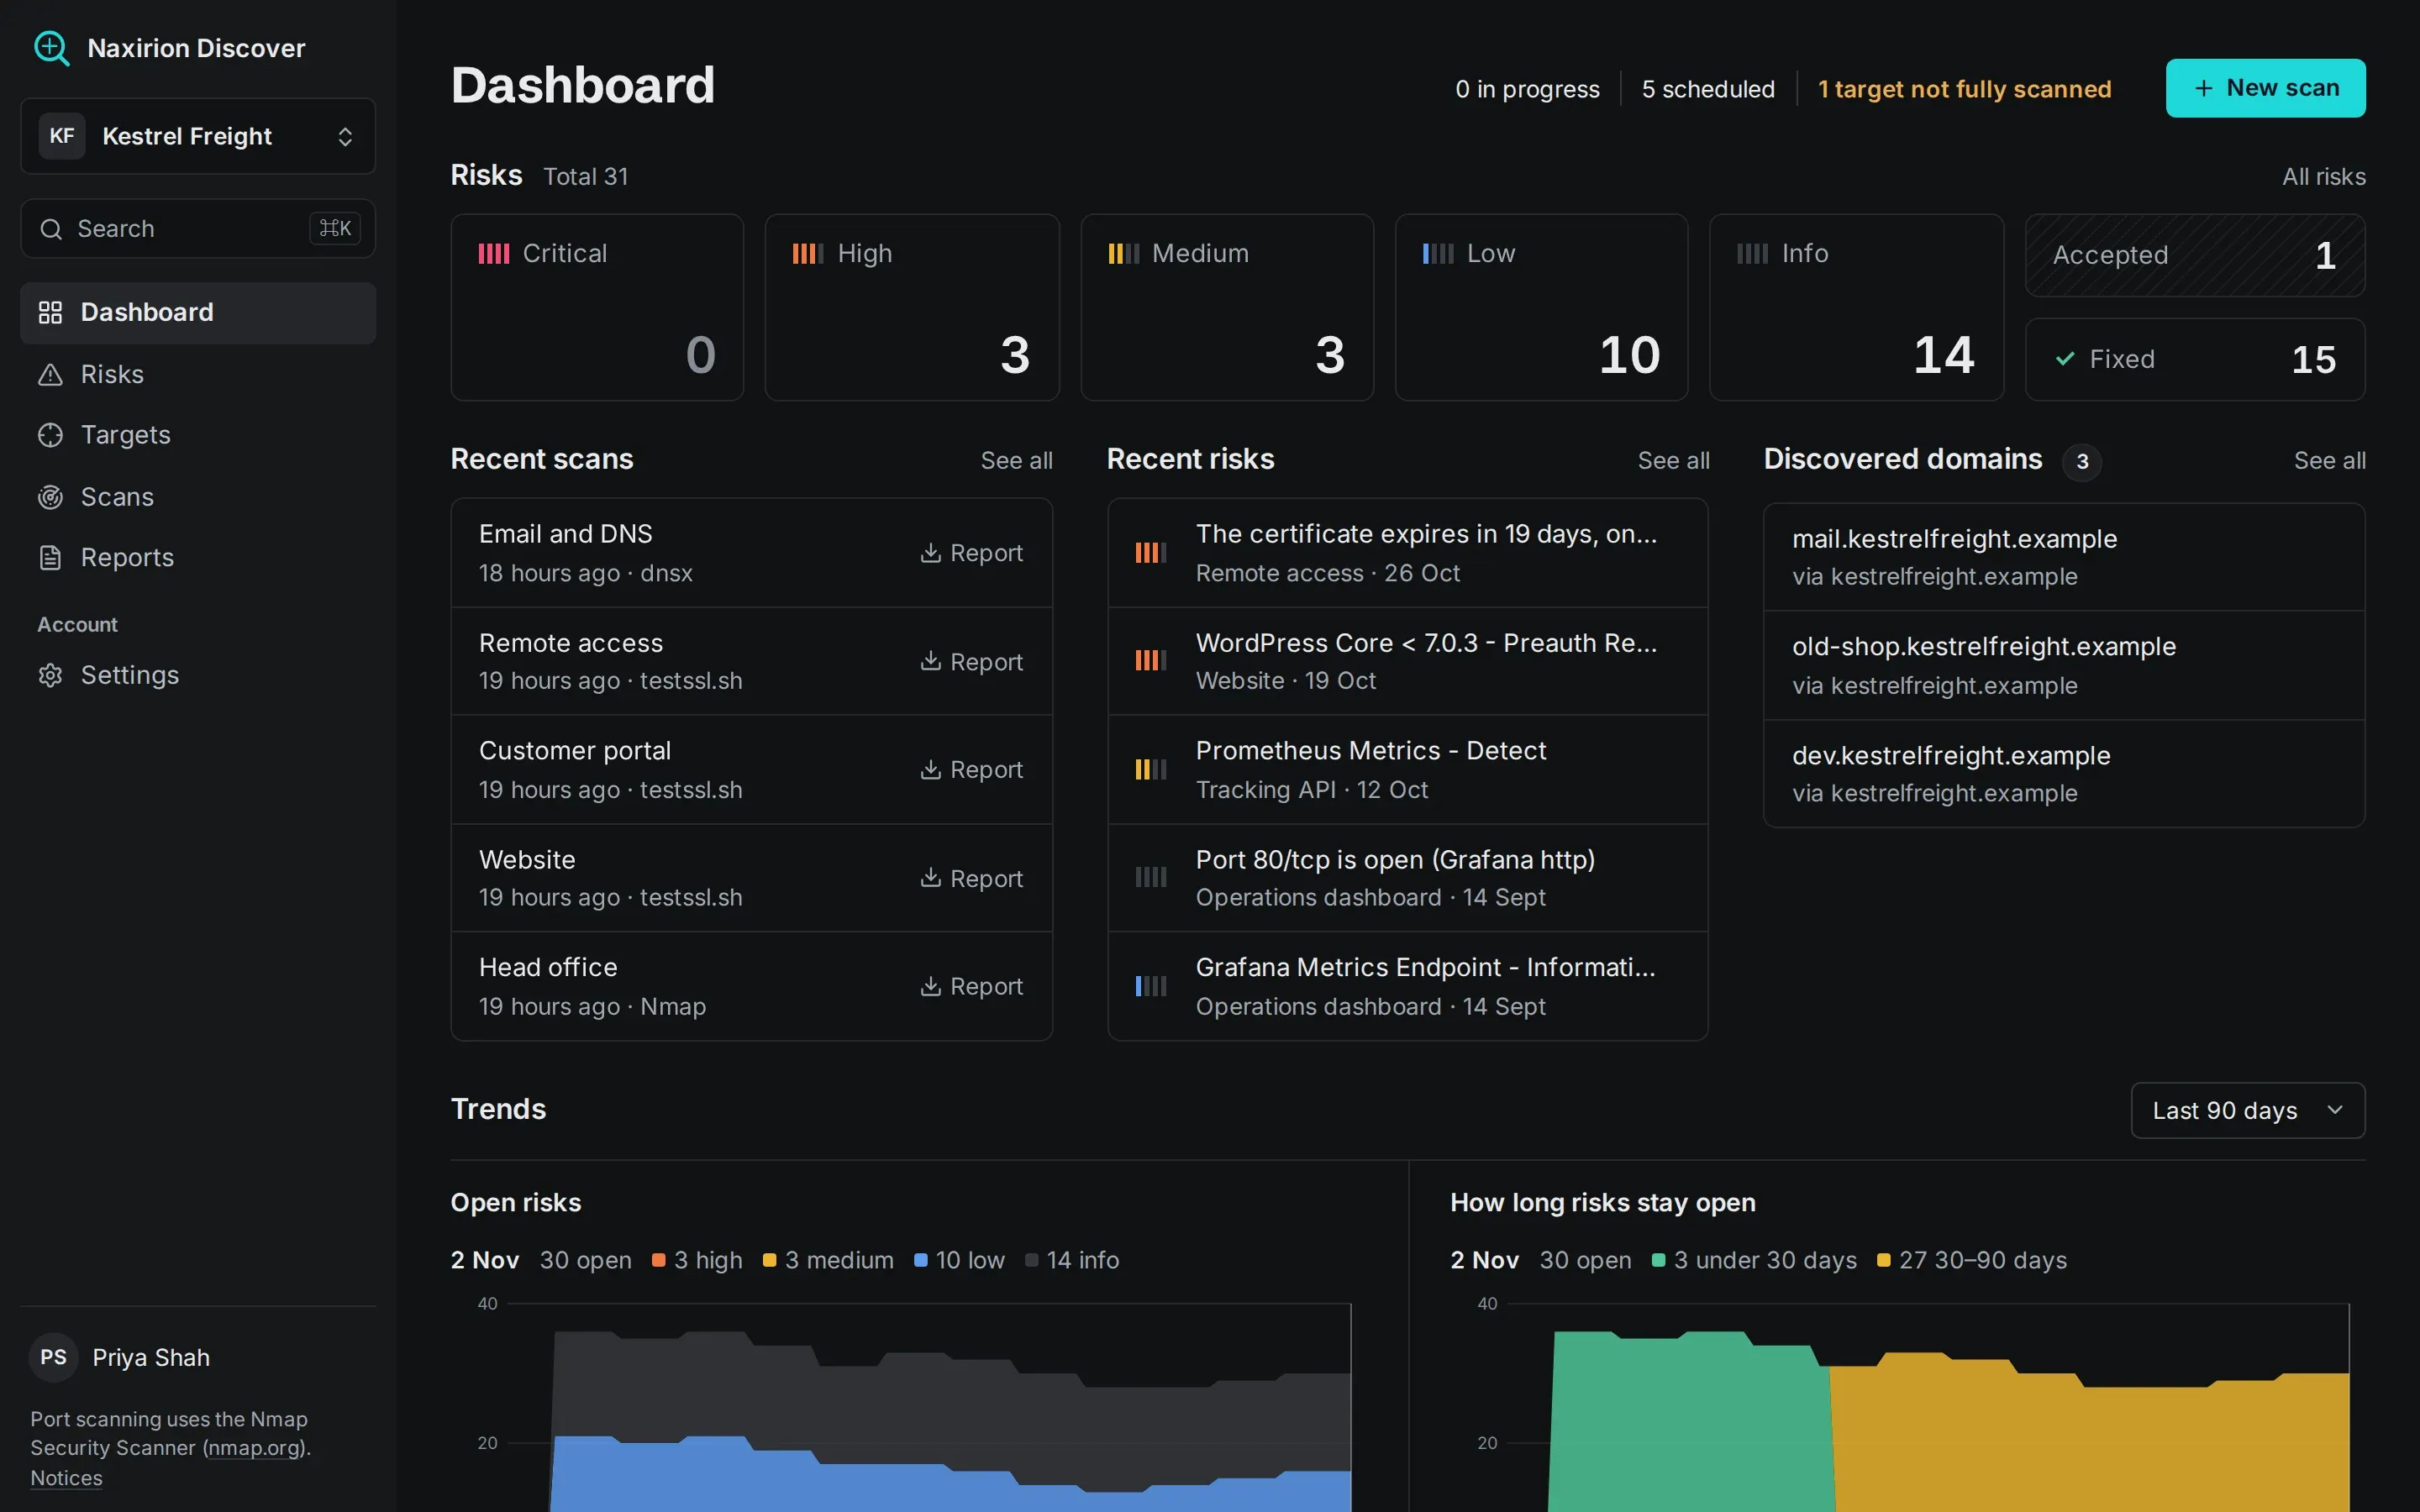
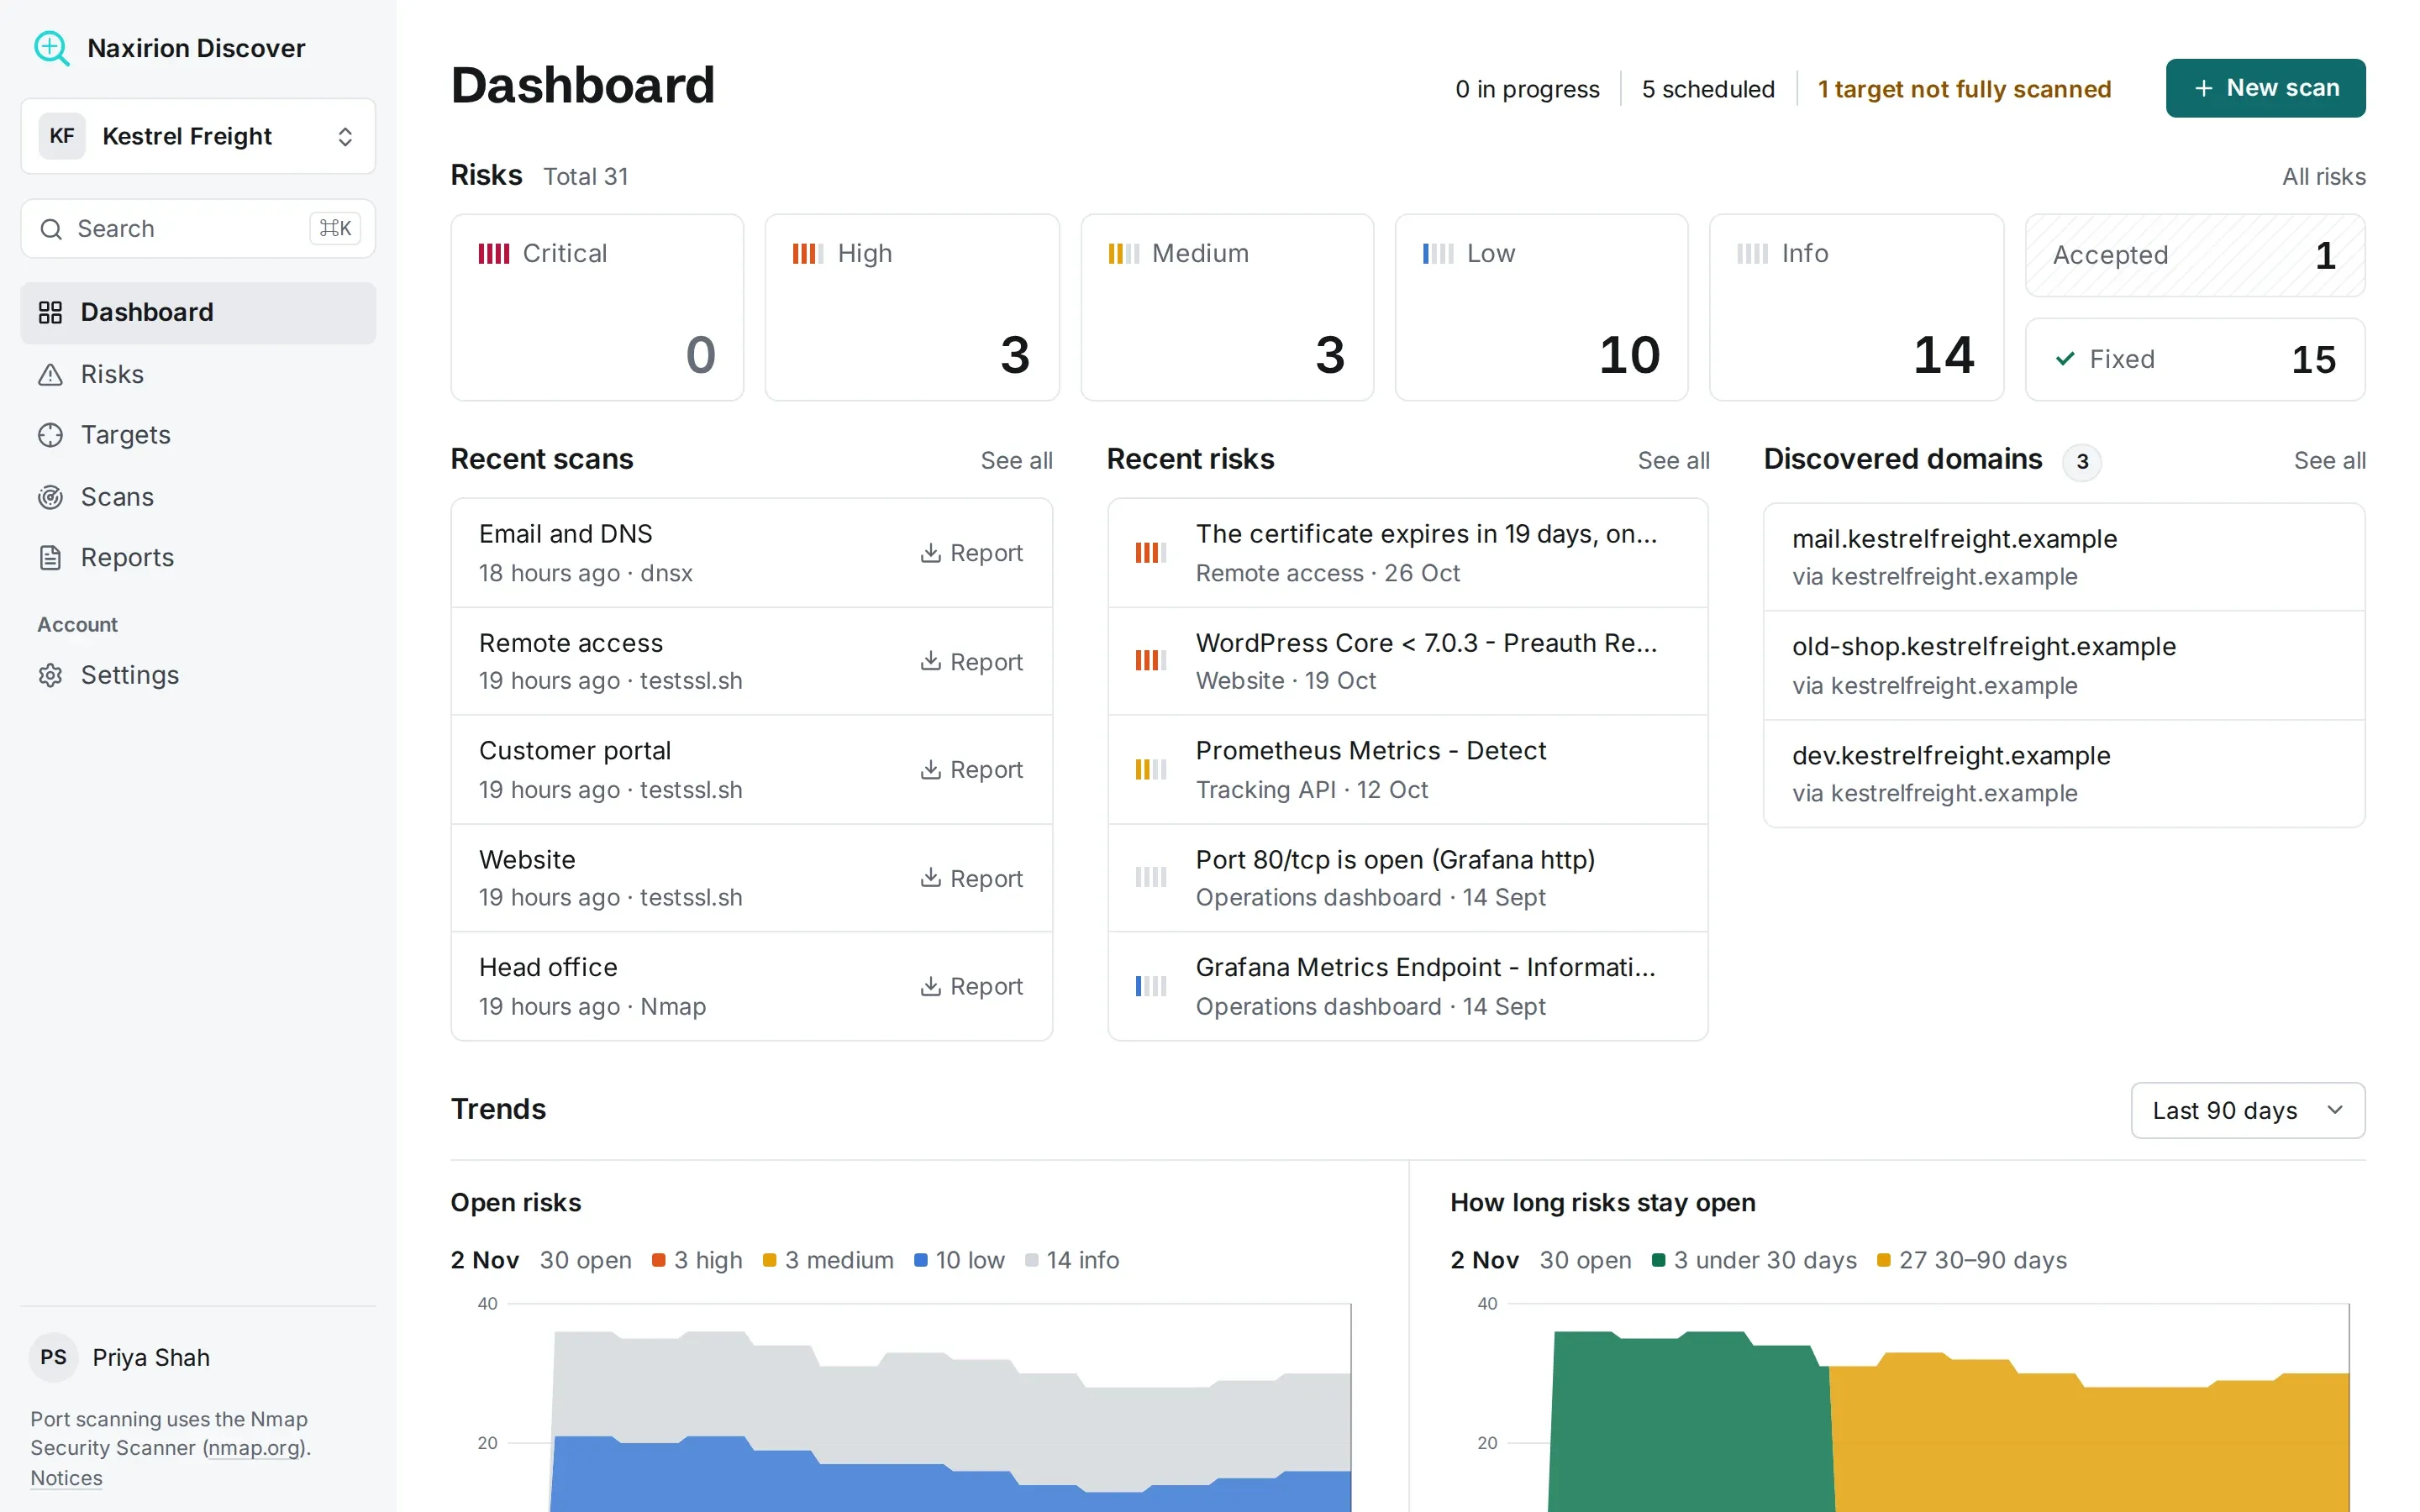
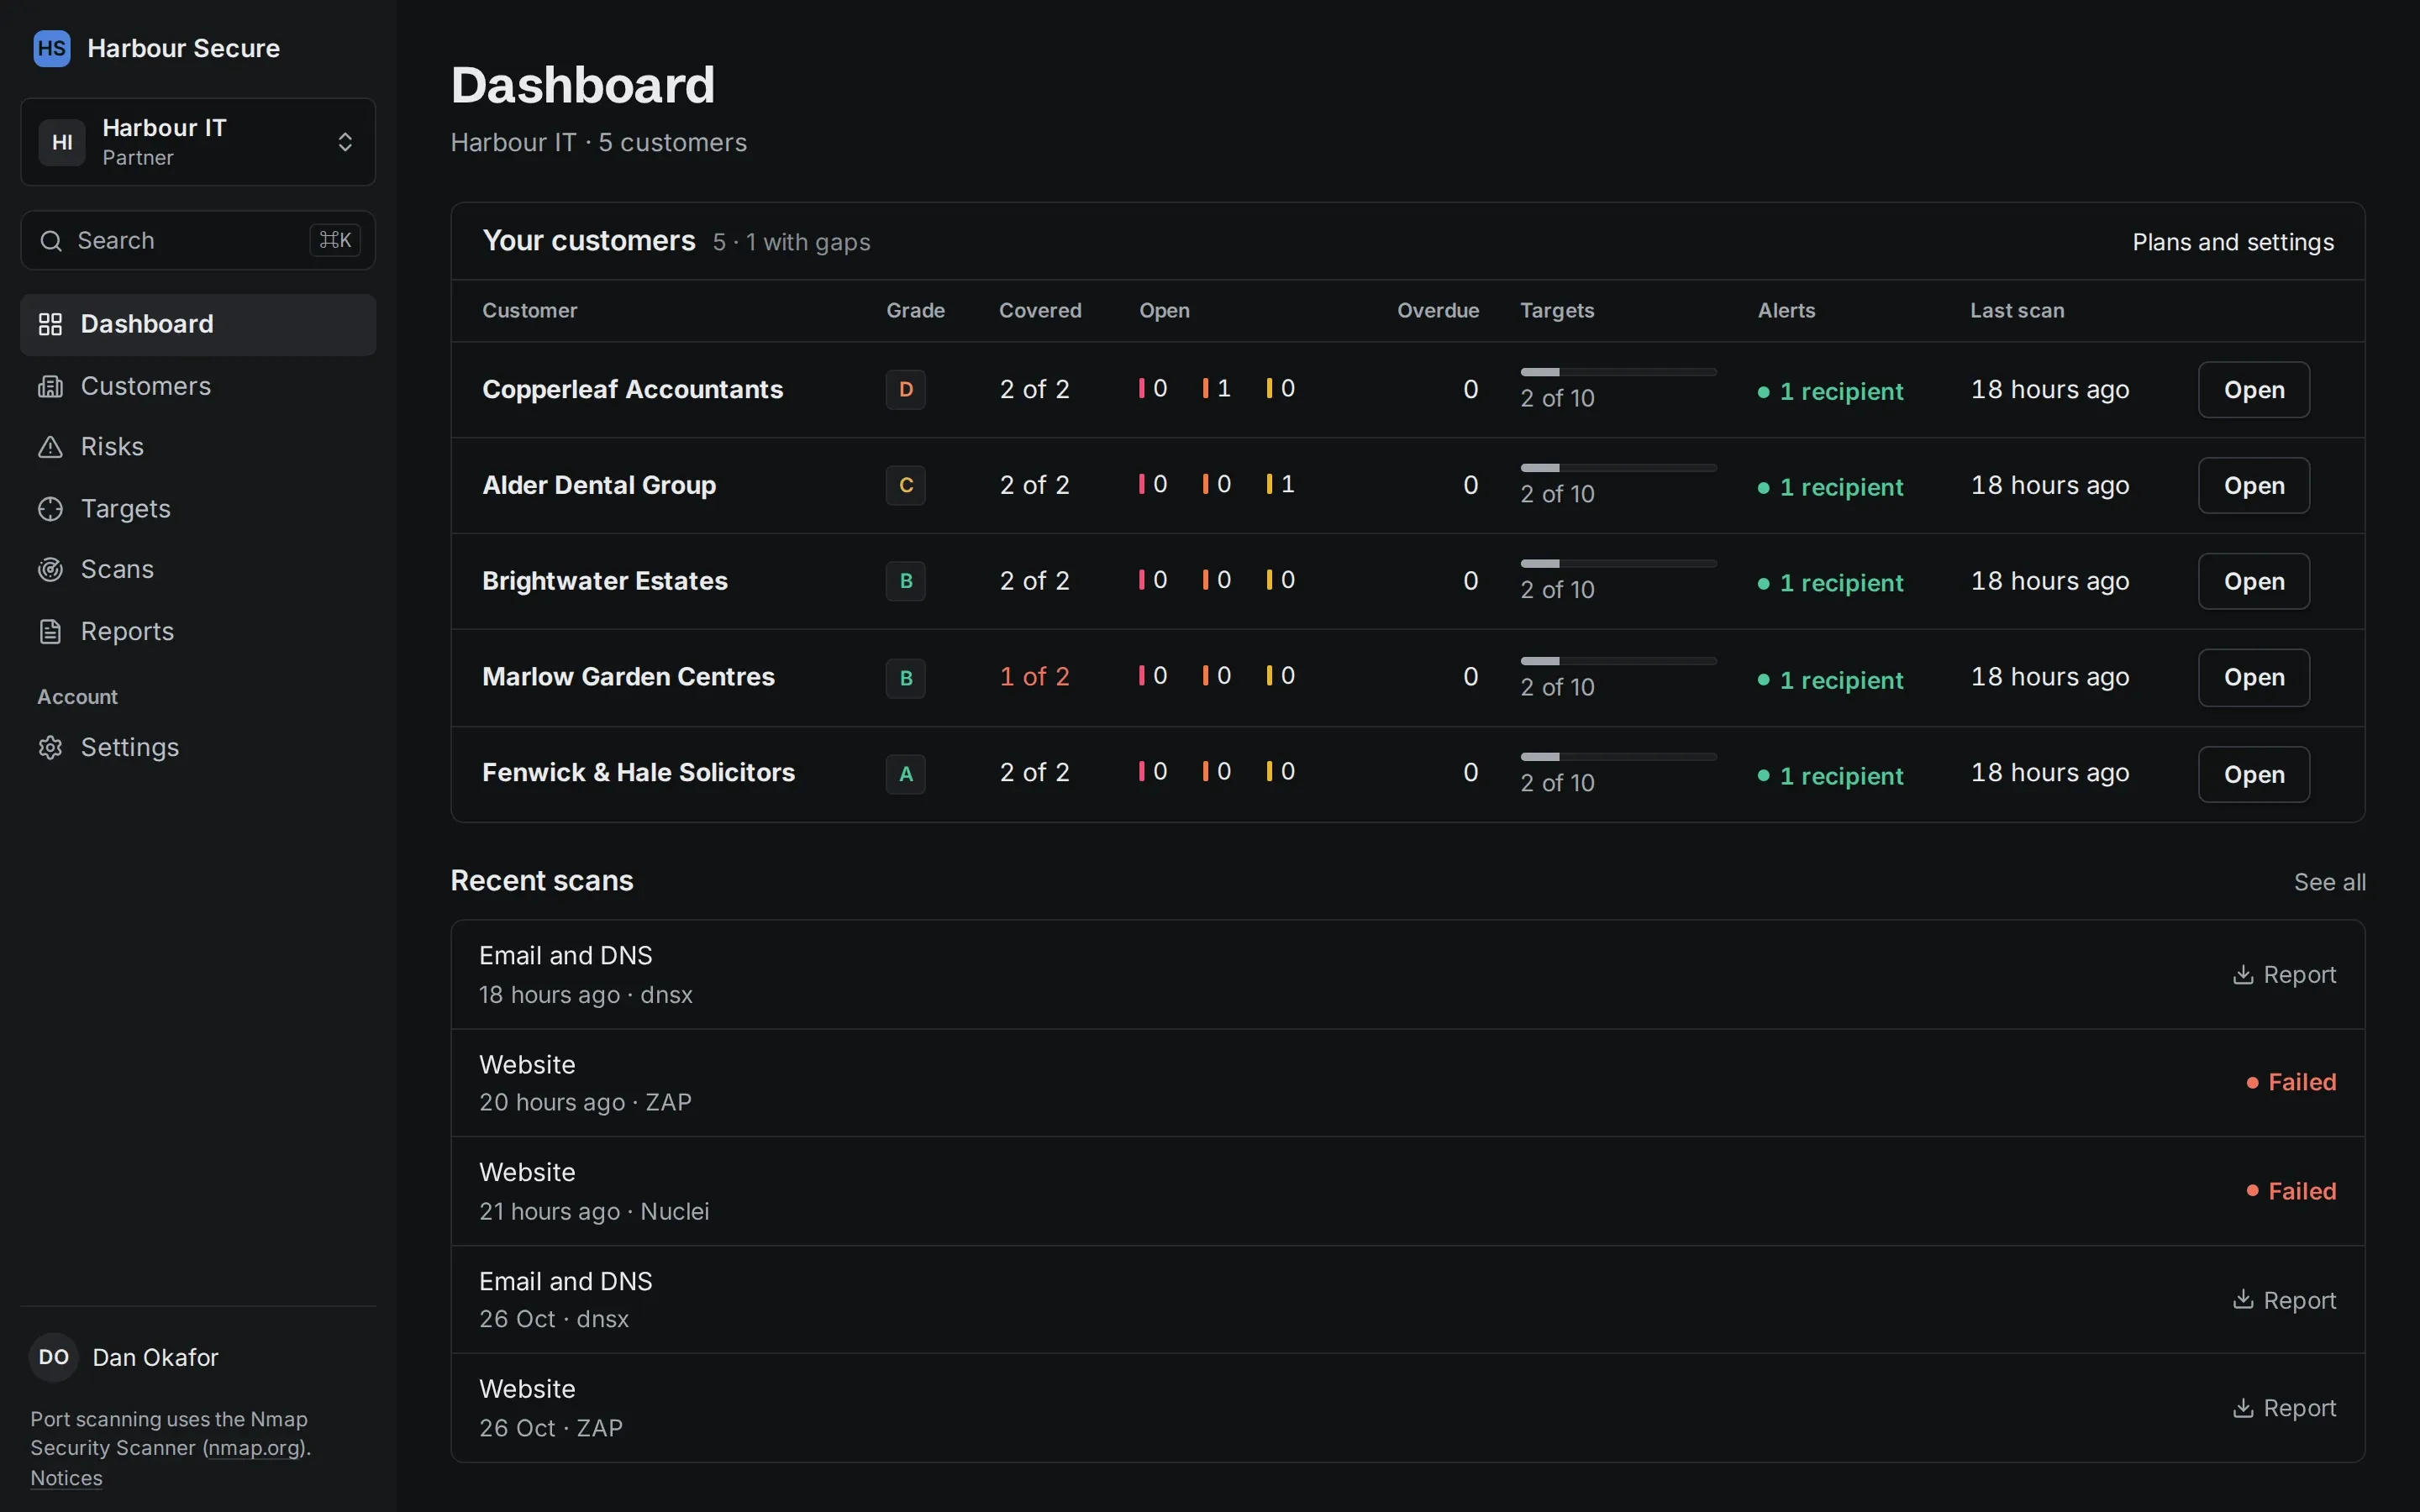
Naxirion Discover with an example account. Every address in these screens is under .example.
What it does
Websites, APIs, every TCP port, encryption, and email and DNS, scanned on a schedule from our scanners, the way anyone on the internet reaches them.
Names under your domains are looked up in certificate logs every week, and discovery flags names still pointing at hosting nobody owns. Nothing new is scanned until you add it.
Every finding says whether CISA lists it as exploited and FIRST's estimate of how likely an attack is, with an owner, a fix-by date and advice in plain English.
One letter for each target and for the account. A target we couldn't scan is named with the reason, and never counted as clean.
Inside the product
Every finding from every engine, written the same way, with what to do about it. The grade sits on top and never covers a target we couldn't look at.
Risks
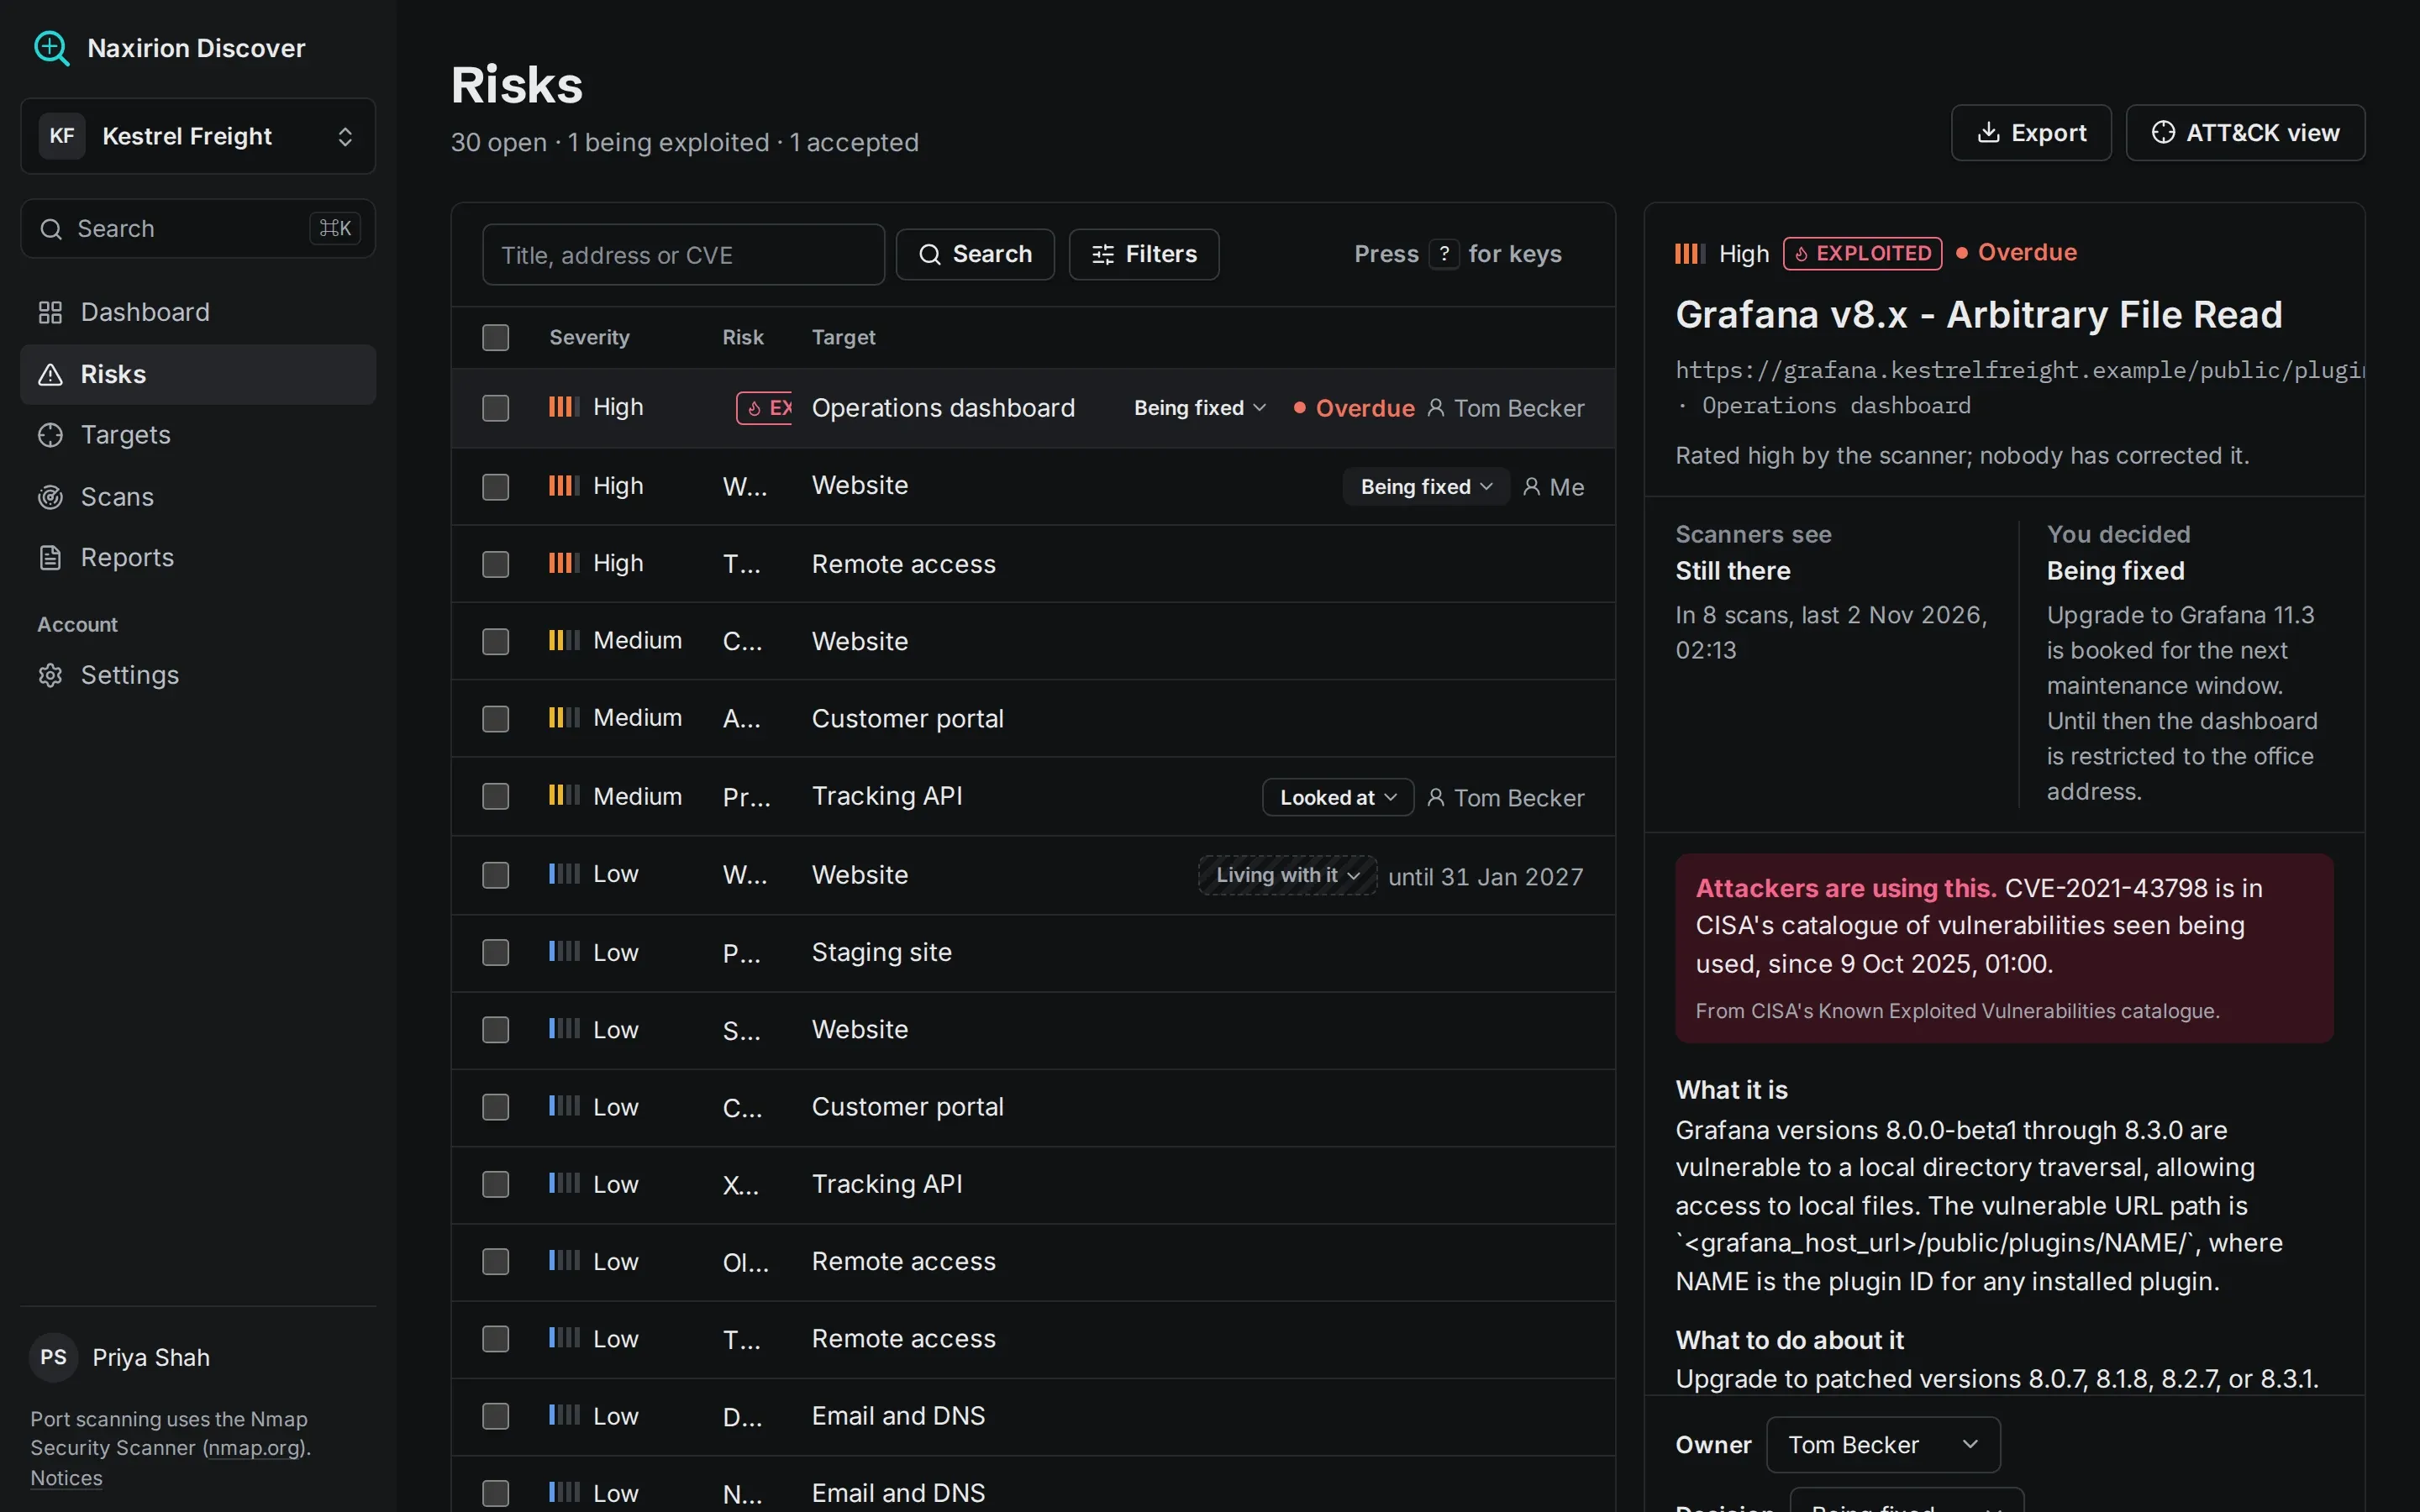
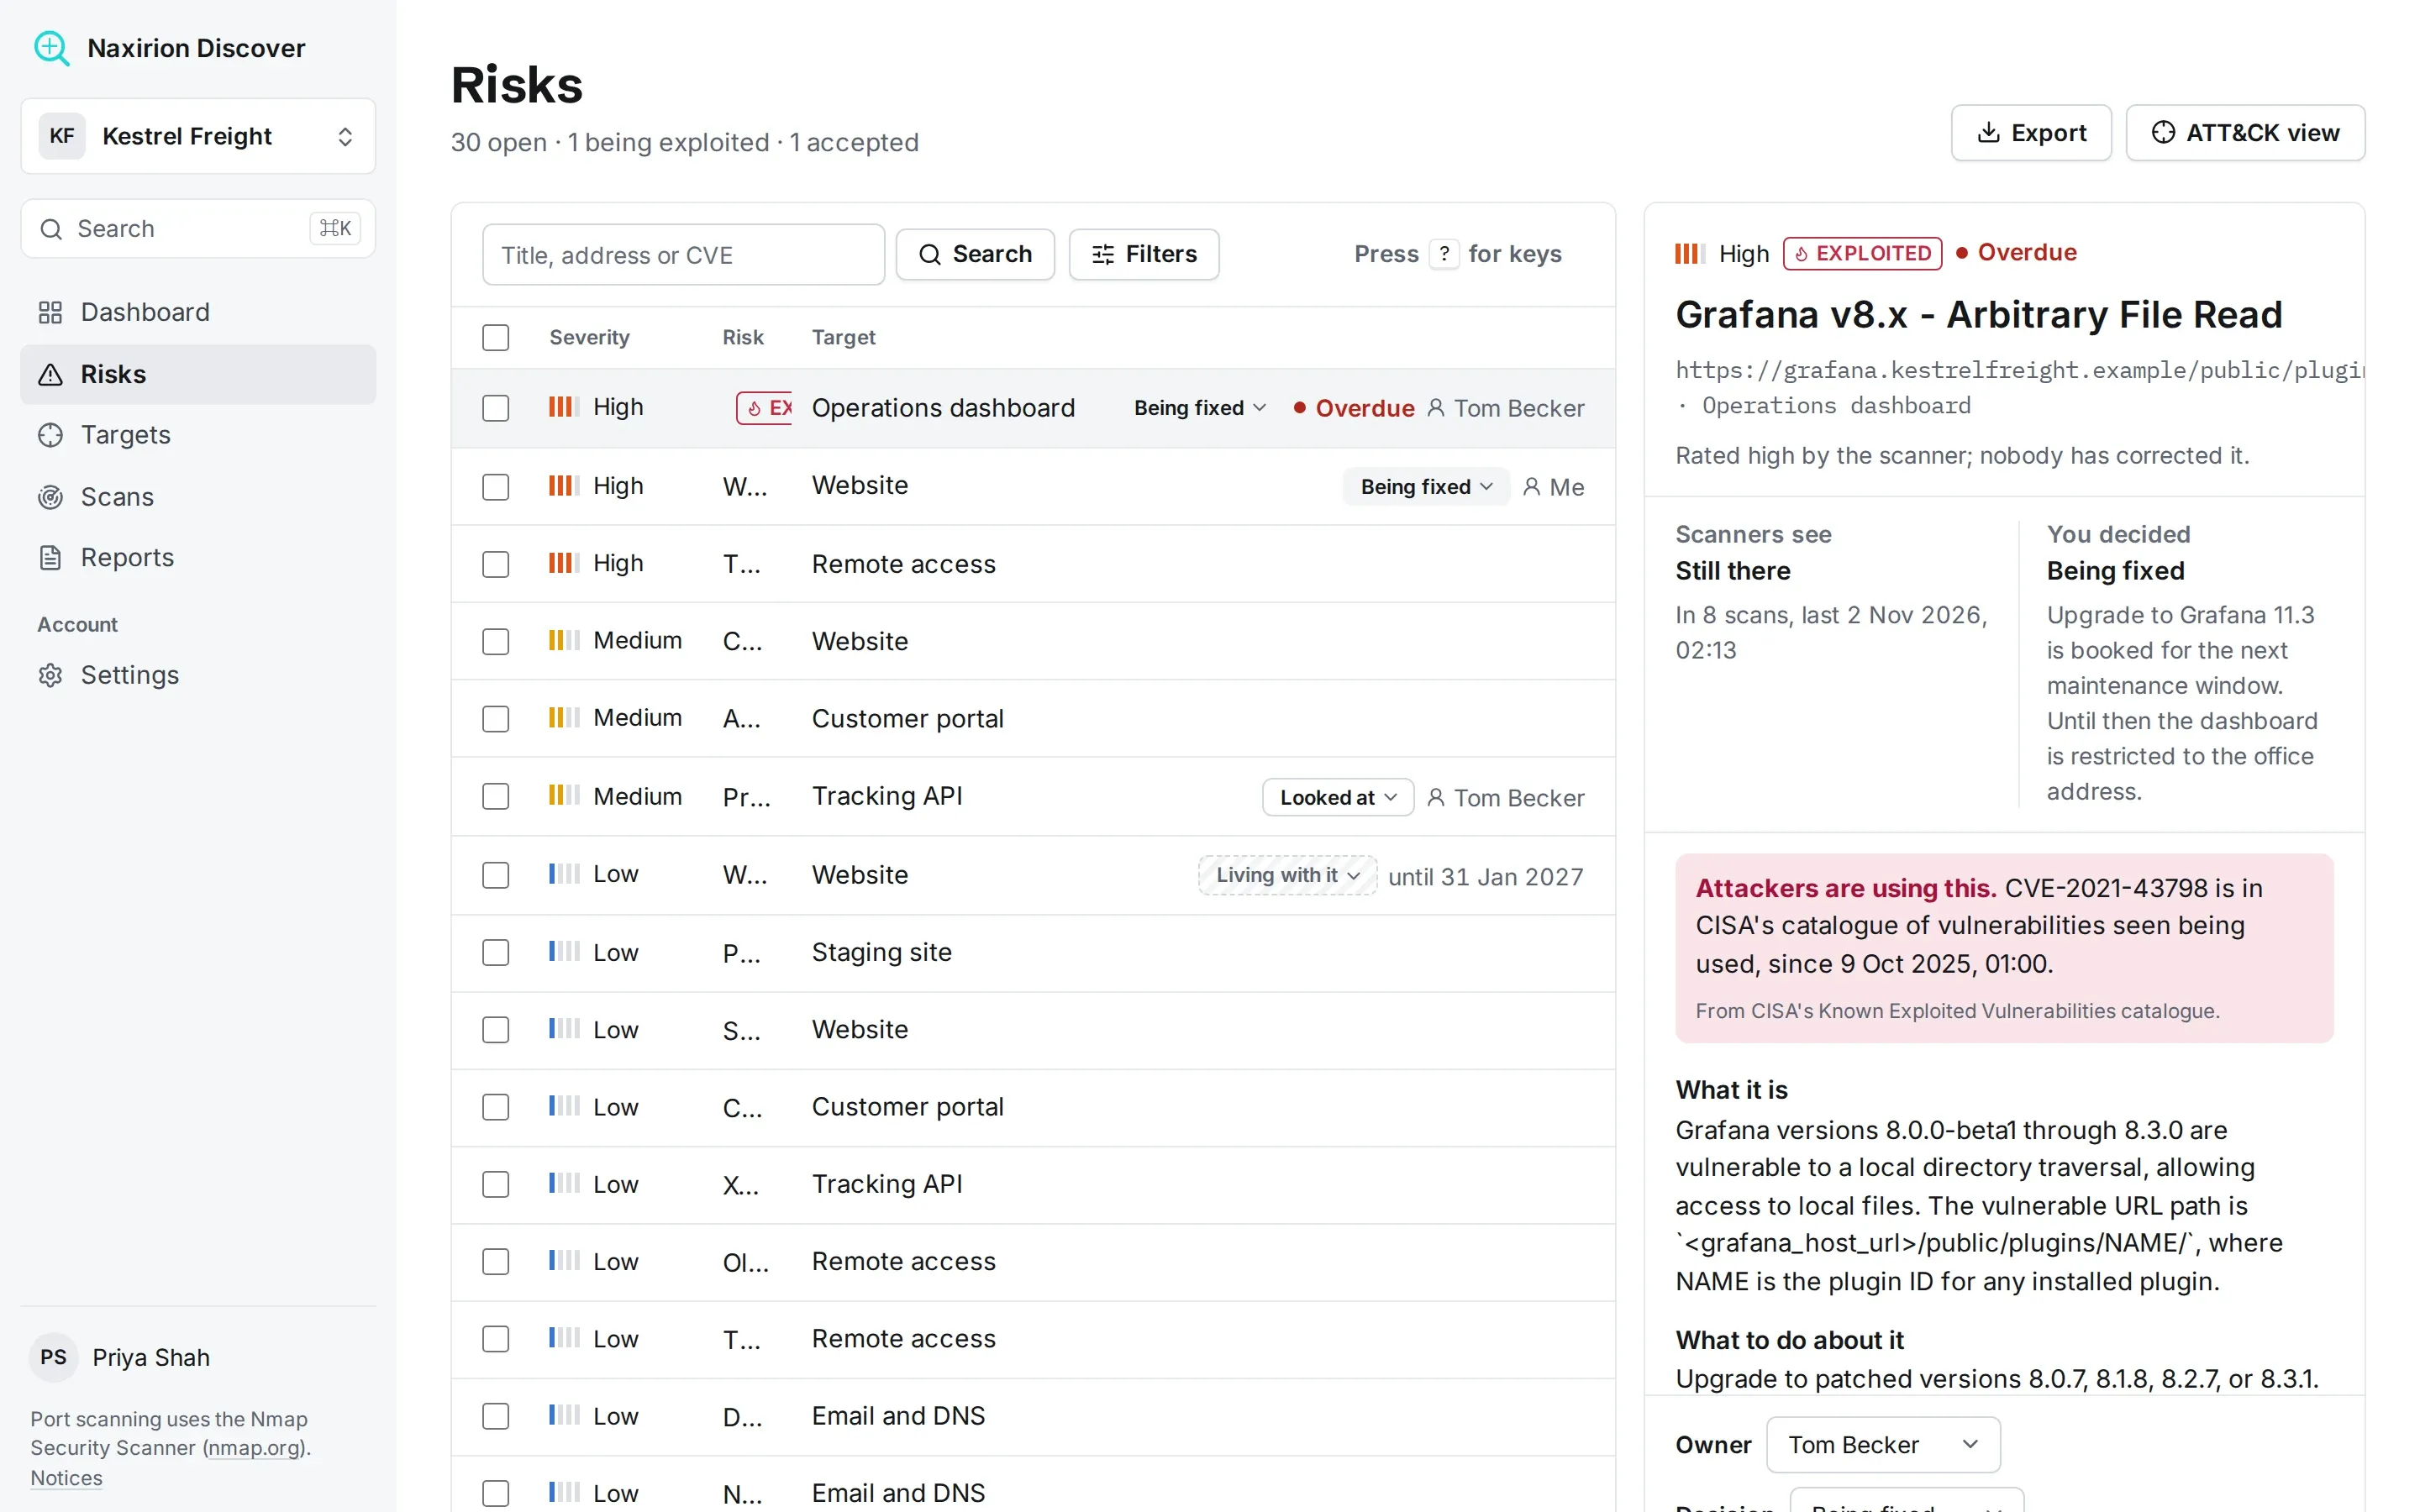
Every finding from every scan lands in one list, deduplicated and worst first. Open one and it says what it is, what to do about it, and whether attackers are using it, beside the severity and never instead of it.
Targets
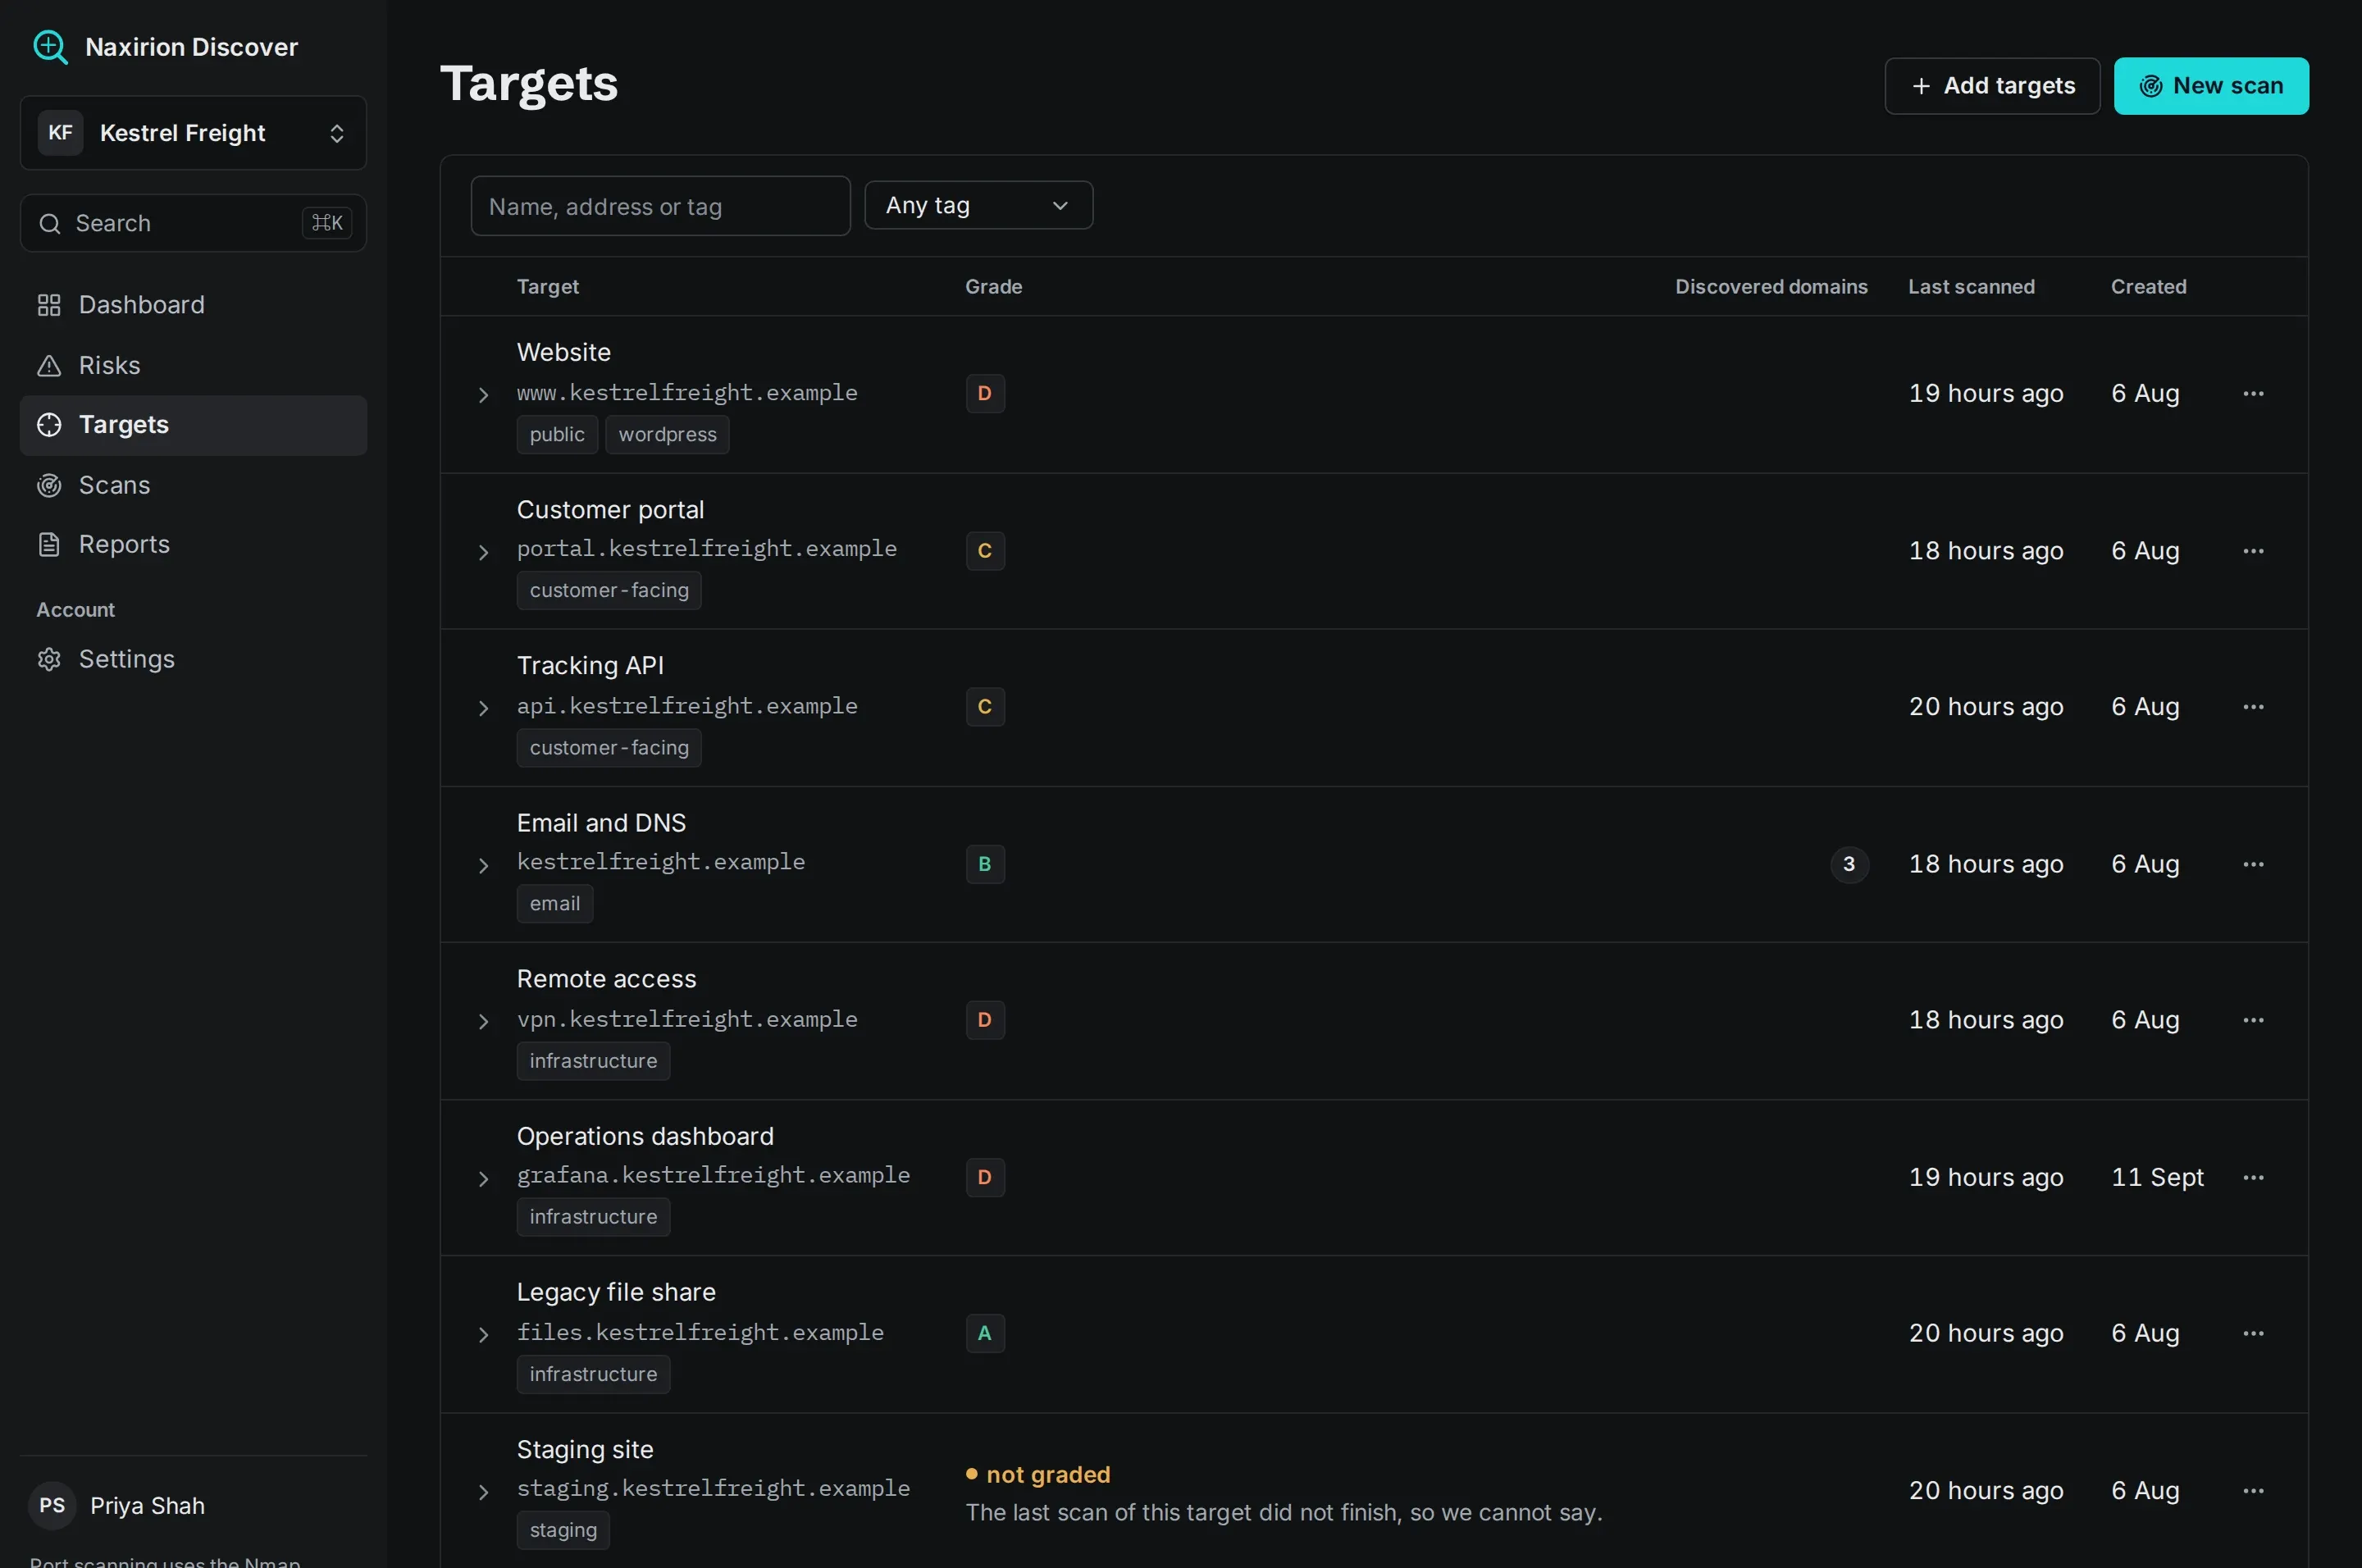
Each website, server and domain is graded A to F by the most serious thing still open on it. A target that couldn't be scanned isn't graded at all. It's listed with the reason and stays in the count, so it can't make your grade look better.
Scans
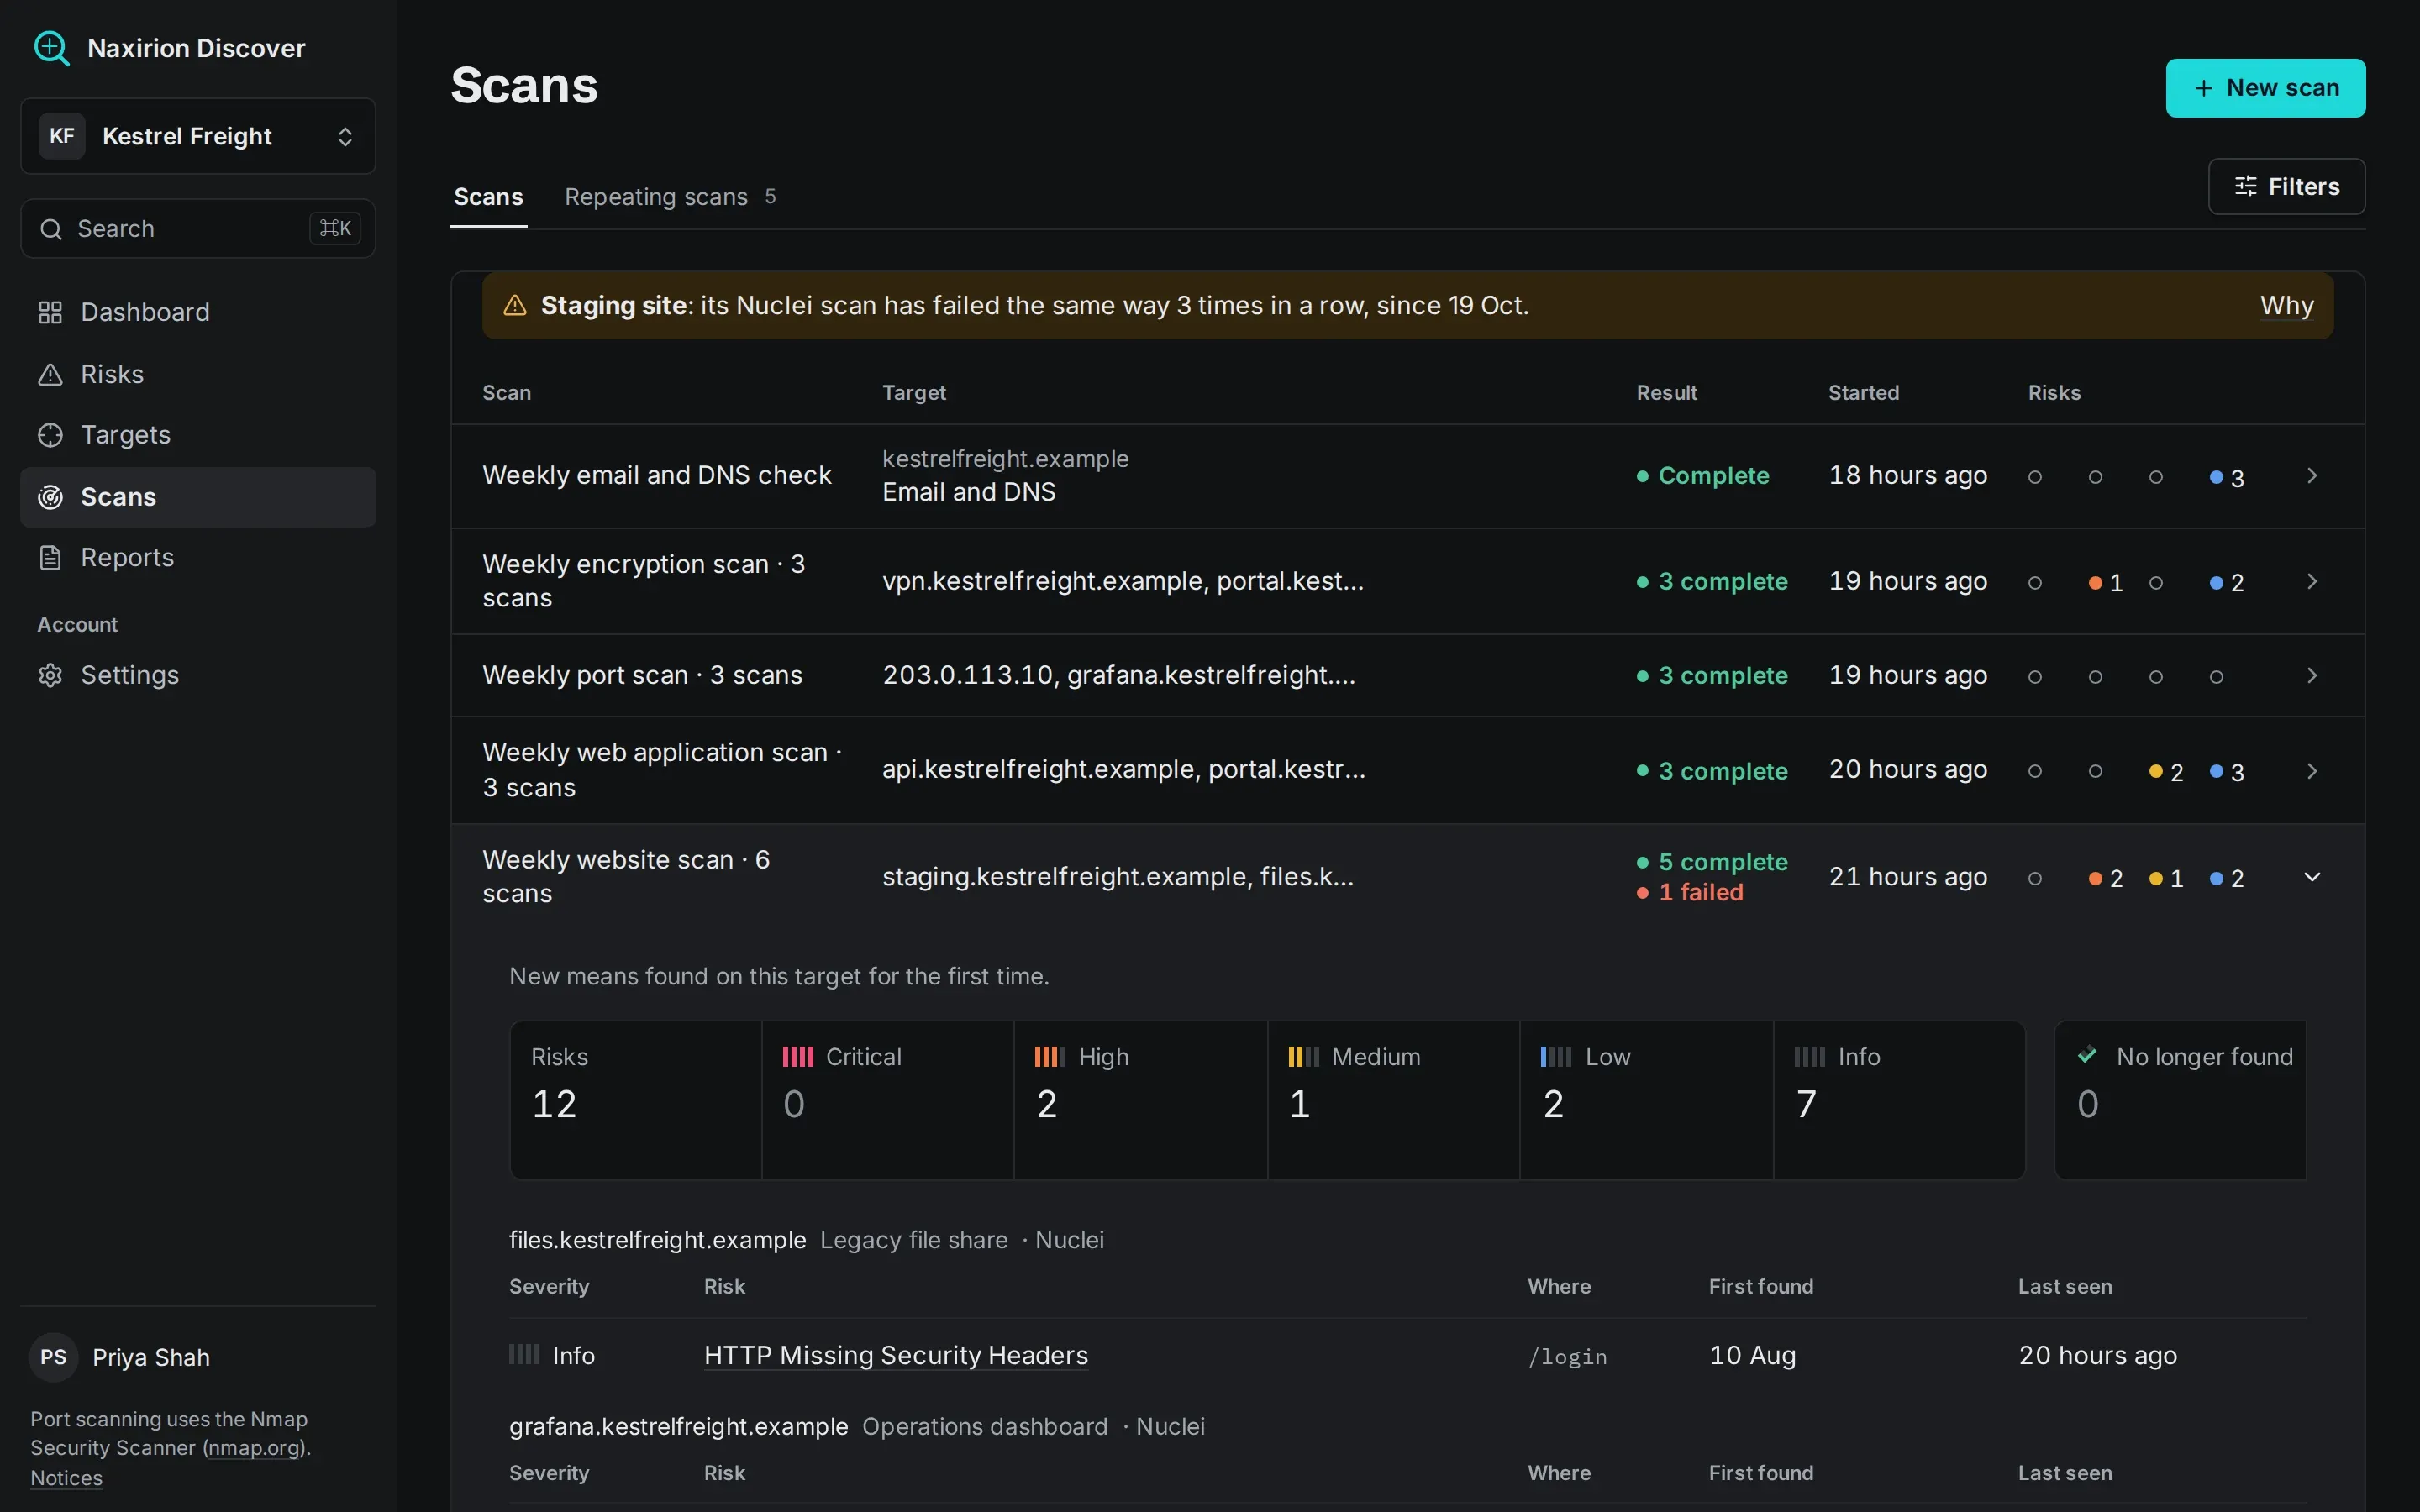
Scans run on your schedule, grouped by what started them. Open one to see what it found, what's new and what it no longer sees. A scan that failed says why, and a failure that keeps happening is said once, plainly, instead of passing for a quiet week.
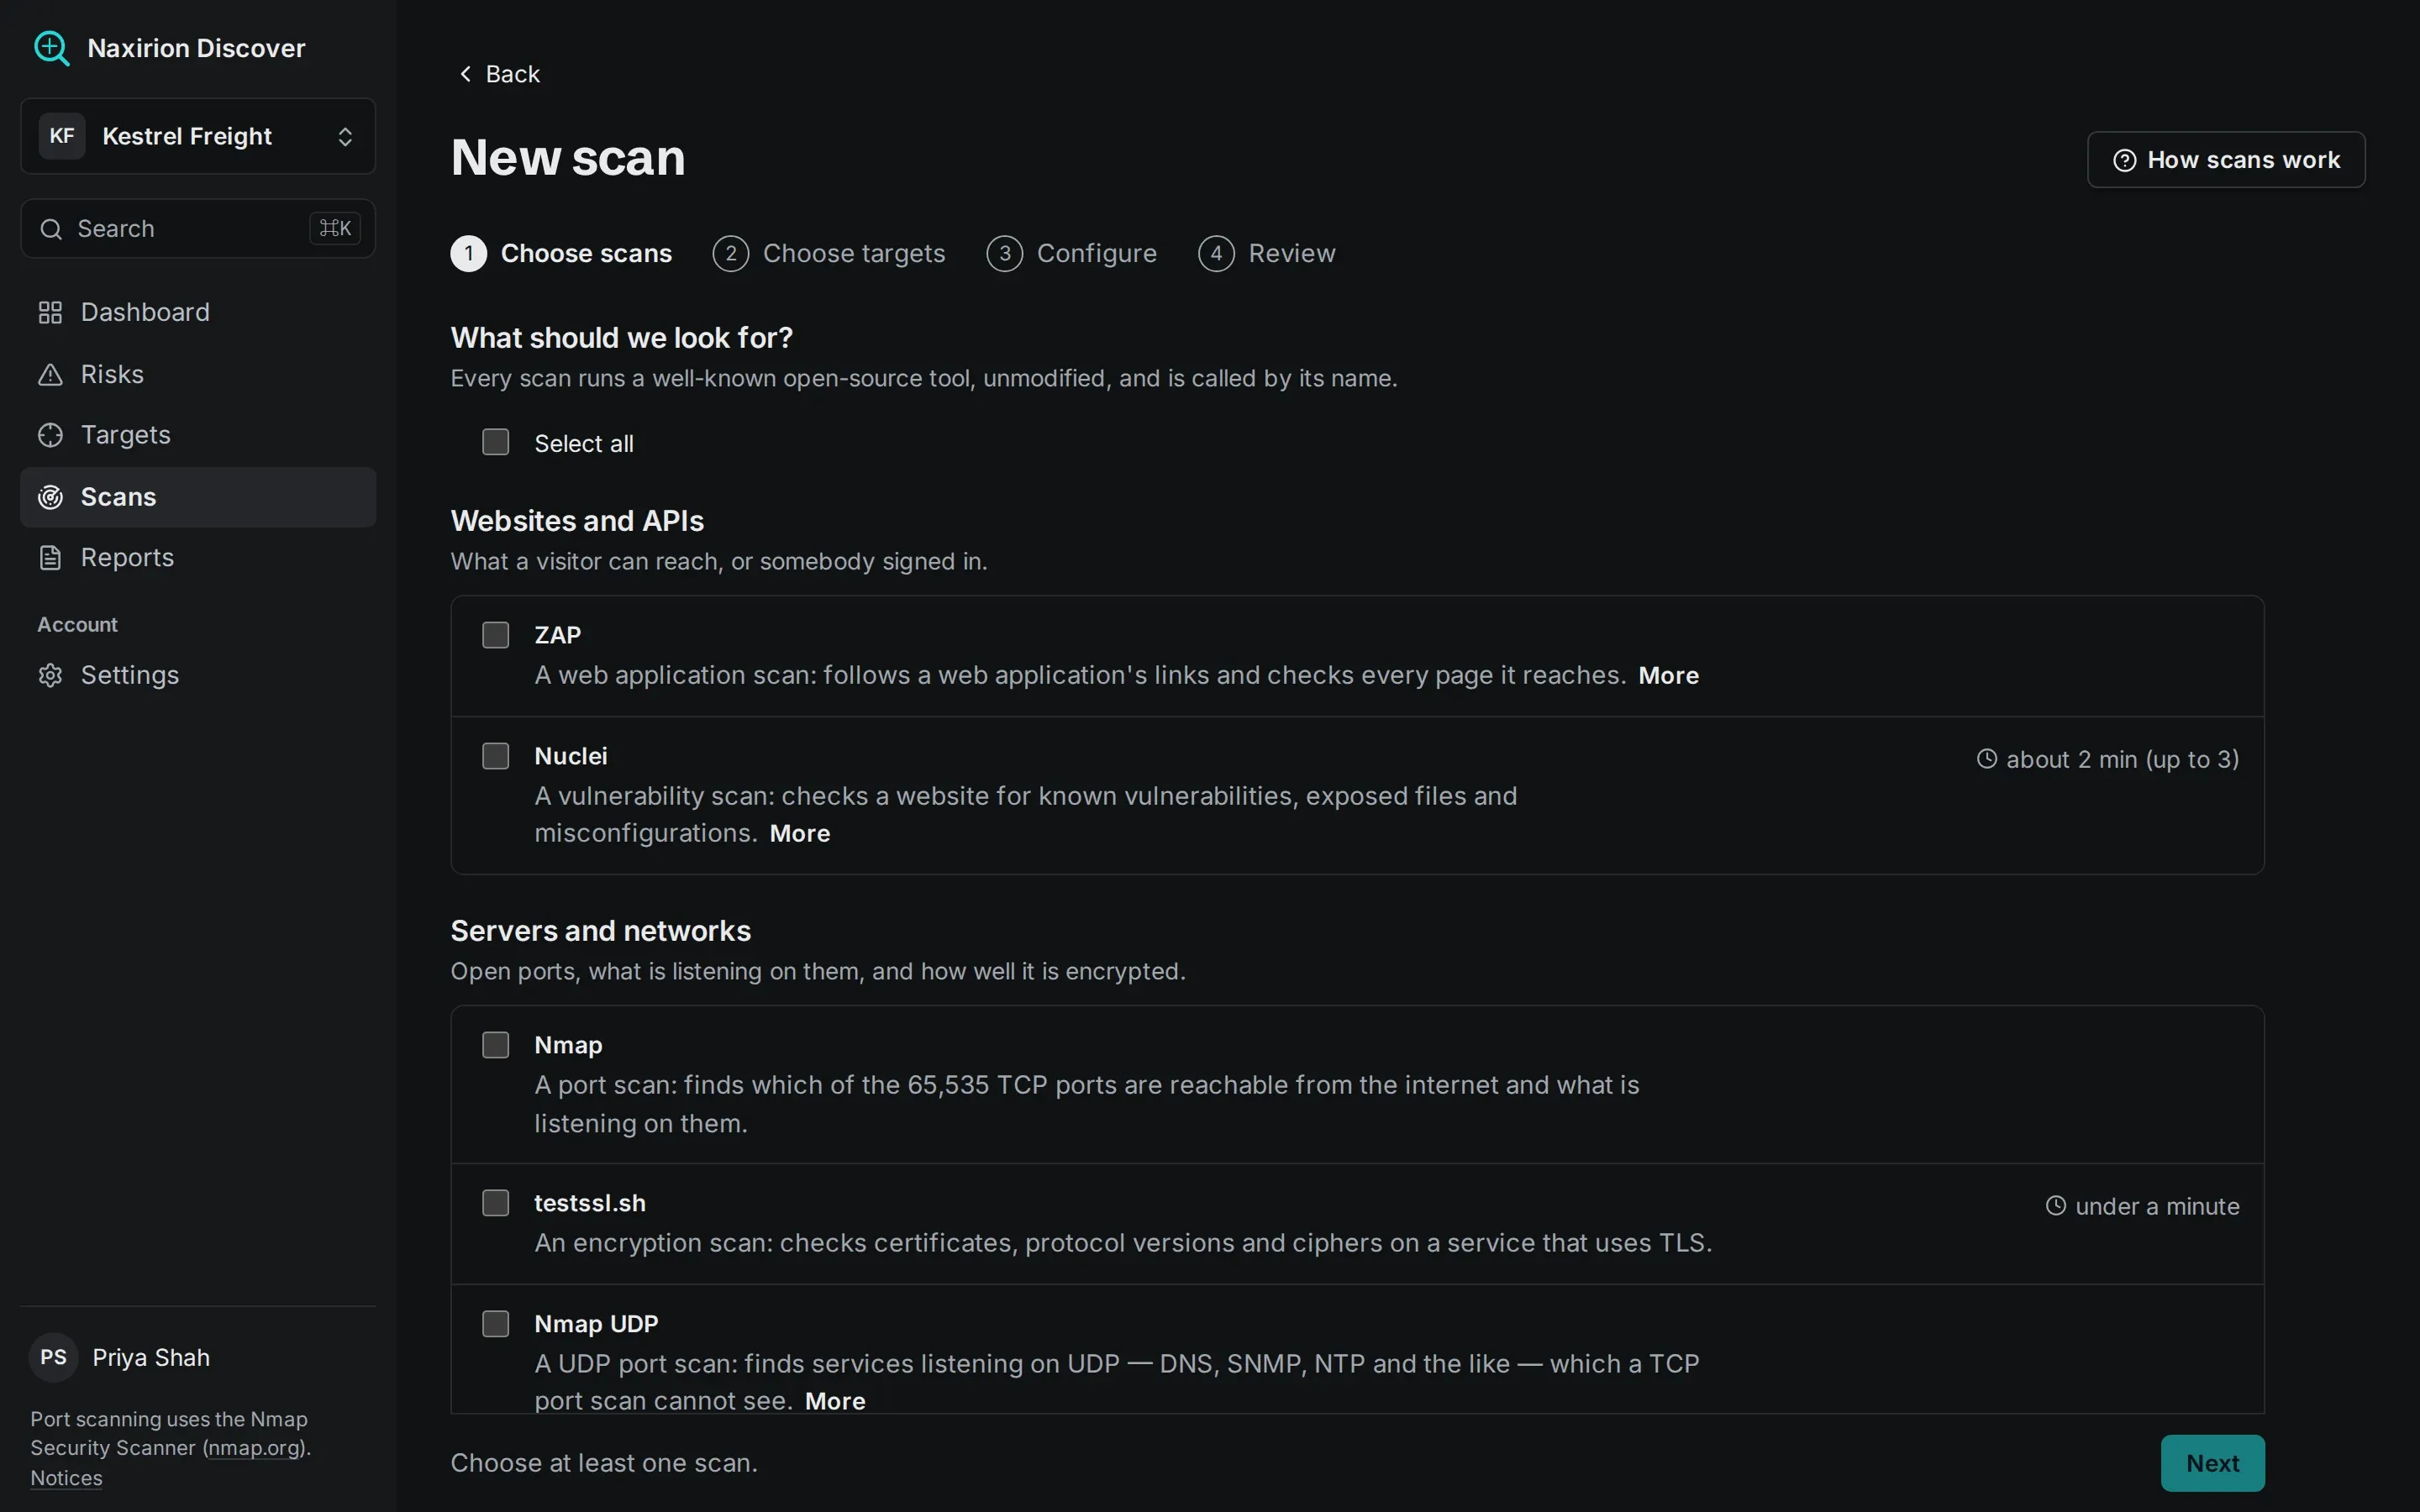
New scan
Pick what to look for and which targets to scan. Each choice is checked as you make it, so a scan that can't run tells you why before you start it. Every scan runs a well-known open-source engine, unmodified.
Reports
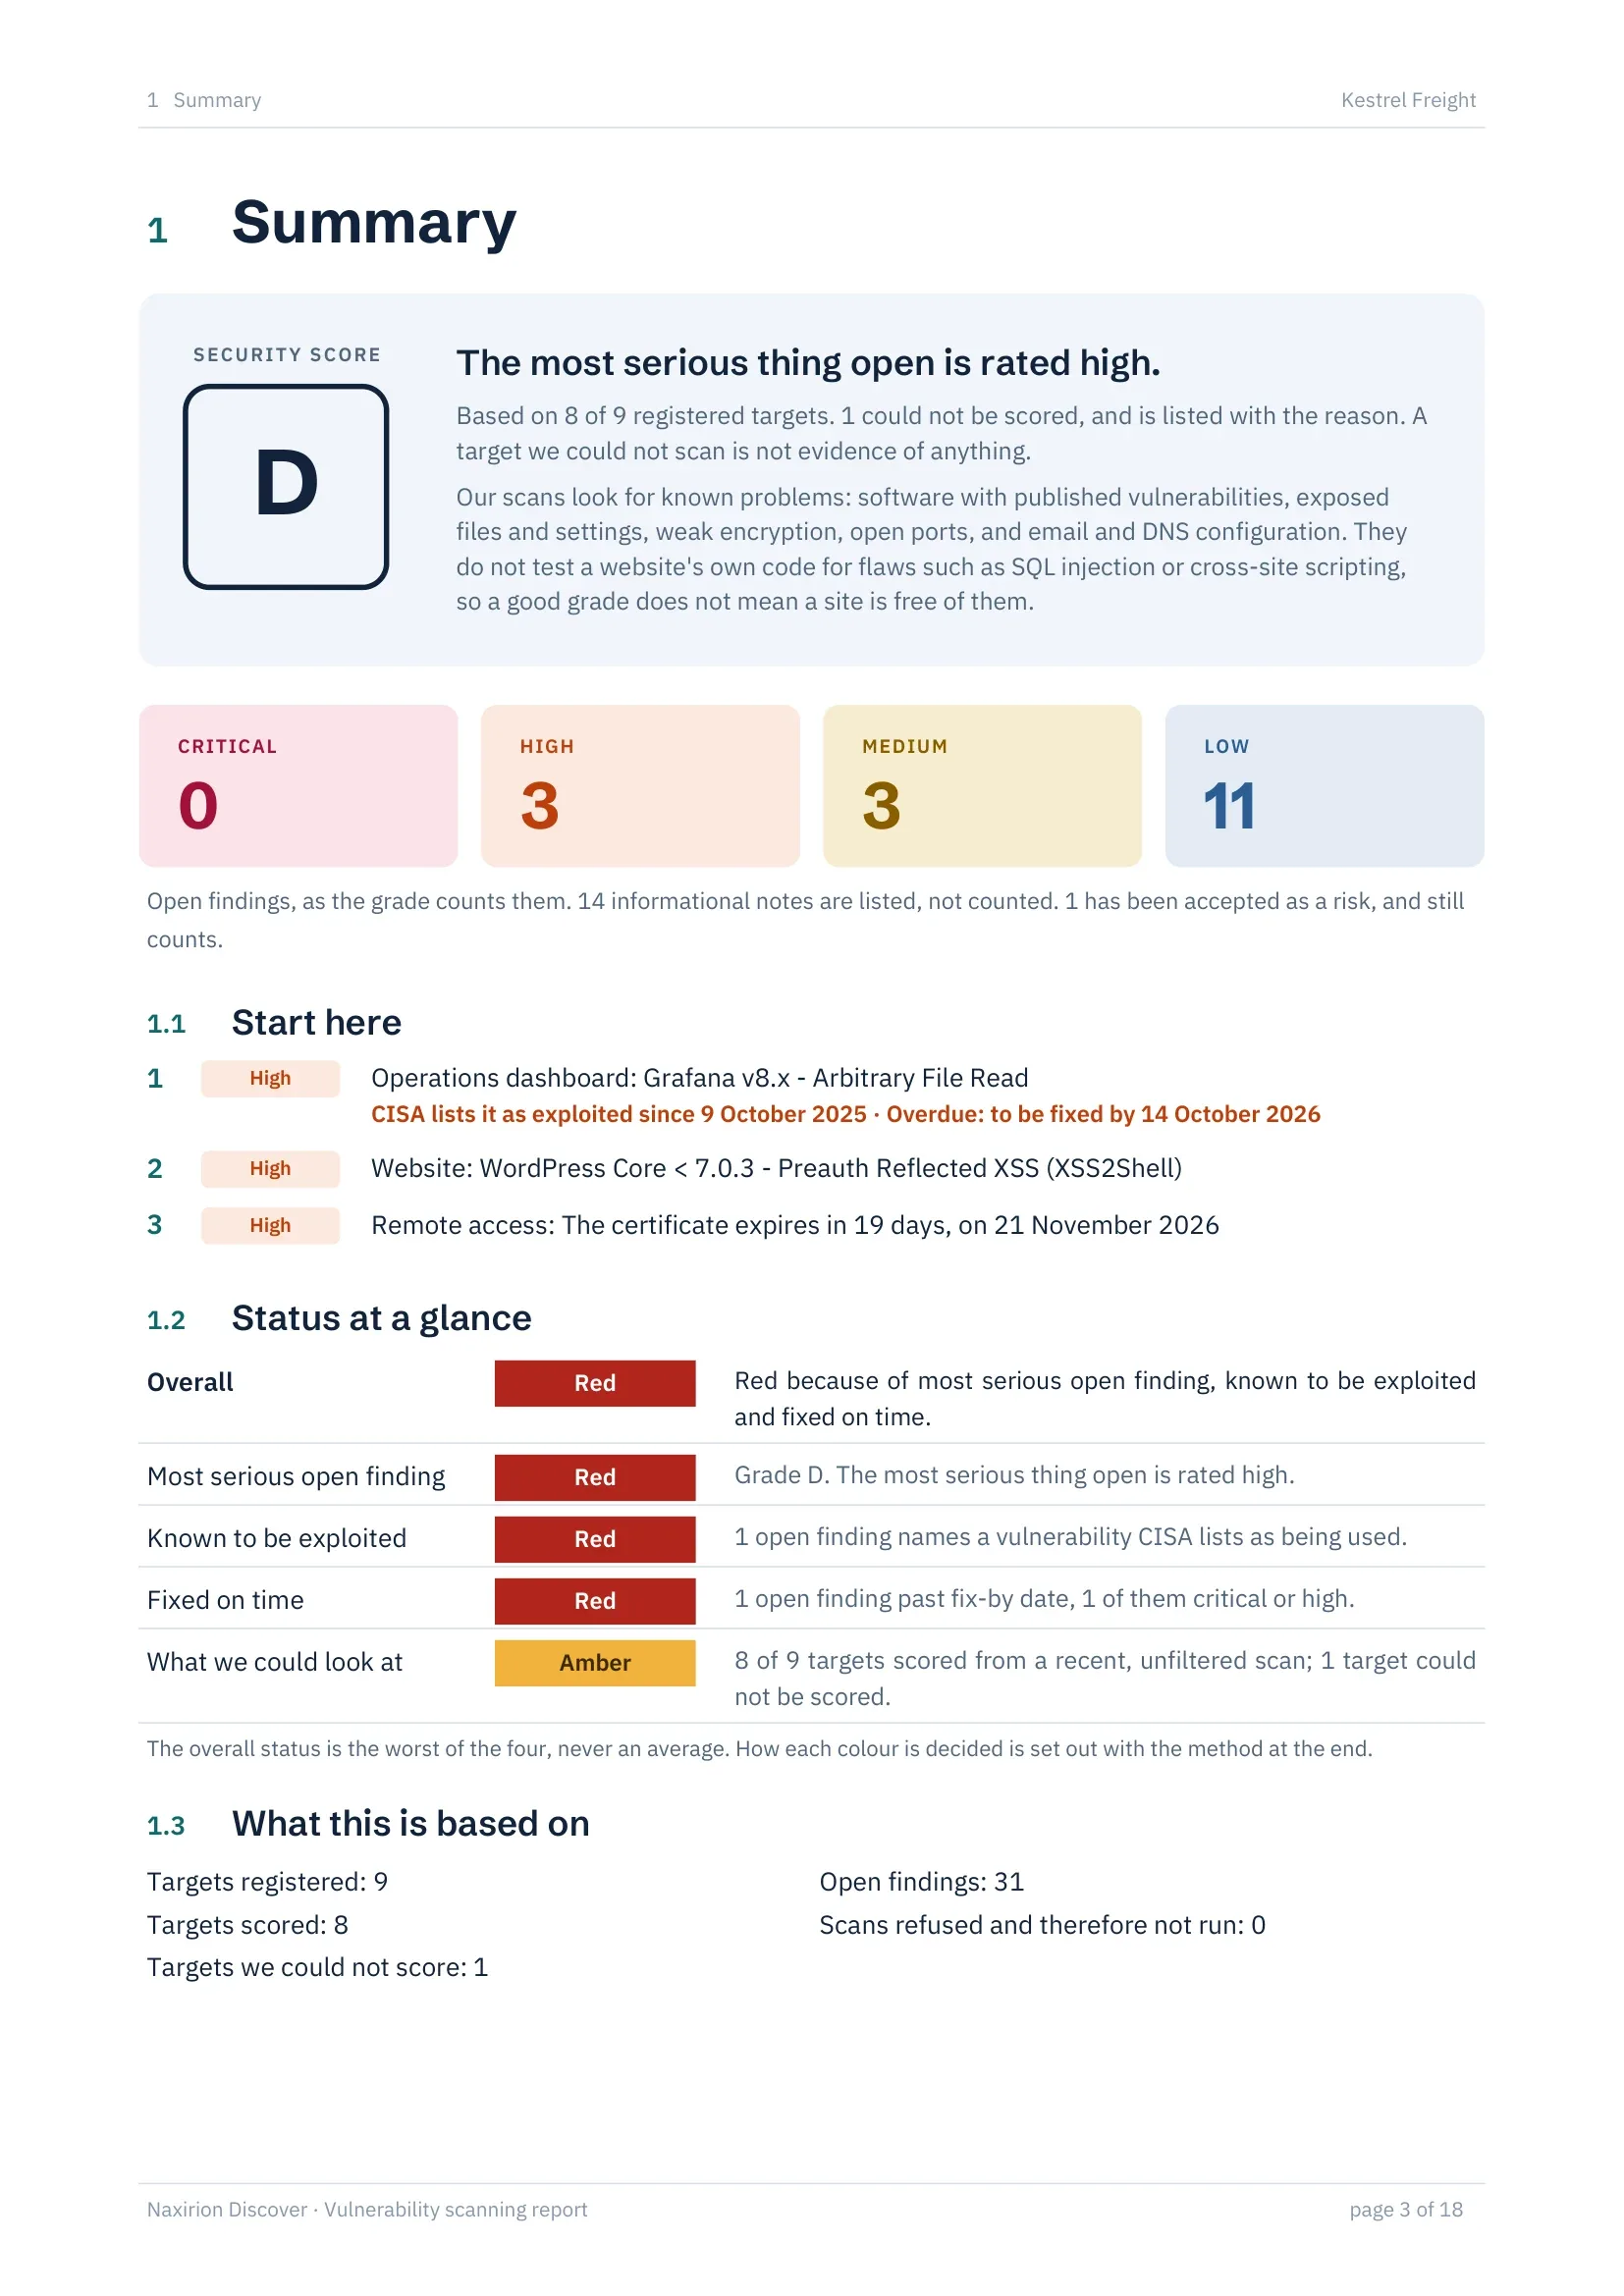
A branded PDF that opens with one page: the grade and what it covers, the three things to fix first, and a red, amber or green status that's never green over a gap. Then a page for each target, the history, and MITRE ATT&CK.
For MSPs
Run scanning for all your clients from one dashboard, under your own name, color and logo, on plans you set. Your clients see your brand on the portal, in their reports and in every email.
What it scans
Each one runs a well-known open-source engine, unmodified, and is called by its name. And every week, without a scan, we look up the names certificates have been issued for under your domains.
Crawls your site, signed in if you give it details, and checks every page it reaches. Passive, or with active tests that submit forms when you choose them.
Websites and APIs
Known vulnerabilities, exposed files, leaked secrets and misconfigurations, from a widely used library of checks.
Websites and APIs
Which of the 65,535 TCP ports can be reached from the internet and what is listening on each, plus services on UDP, such as DNS, SNMP and NTP, that a TCP scan can't see.
Servers and networks
Certificates, protocol versions and ciphers on any service that uses TLS, with one finding per problem.
Servers and networks
SPF, DKIM, DMARC, MTA-STS (its policy fetched and checked, not just the record), TLS-RPT, DNSSEC and CAA.
Domains and email
Names under your domains from public sources, and names still pointing at hosting nobody owns any more.
Domains and email
The Nmap, ZAP and Nuclei names and logos belong to their projects. Naxirion isn't affiliated with or endorsed by them.
Where results go
Besides new risks, you hear when a scan doesn't finish or a schedule stops running, because nothing looks wrong when that happens. A message that never arrived is shown as undelivered, never as sent.
What it doesn't do
Flaws such as SQL injection in software you wrote need a penetration test. Every grade says so.
Discover looks at what faces the internet, from outside, the way an attacker would reach it.
We see what a server shows the network, not the patch levels on it.
Nothing is scanned until it's added as a target, on the account owner's word that it's theirs to have scanned.
Or in a bundle
Know what you have, keep it patched, and stop threats on every endpoint.
Compare bundlesFor MSPs
Partners can white-label Naxirion Discover and offer it to clients under their own name.
Partner programPairs well with
Book a demo and we'll walk you through it and show how it fits with the rest of your security stack.